Operational transparency: why the old privacy model fails
Privacy controls were built for a visible relationship. Digital systems now identify, infer and transfer before the individual knows who is accountable, so transparency has to move earlier.
Traditional privacy controls were built around a visible relationship. An individual is aware of the organisation, receives a privacy statement, makes a choice, and then provides their information.
Digital systems now work in a different order. Identification, analytics, AI processing, inference and cross-border disclosure can all begin before an individual understands who is accountable, what is being processed, or what authority is being claimed. A privacy statement read after the fact comes too late. By then the individual has often been identified, profiled and passed to other organisations.
Four ways the order breaks
Early processing. Websites, apps, devices and sensors can begin collecting signals, assigning identifiers or routing data before an individual logs in, completes a transaction or knowingly begins a relationship.
Early identification. Systems can identify, profile, link or infer information about an individual before the individual has any access to notice or consent. Transparency has to move to before the moment of identification and inference.
Many actors. Processing involves platforms, cloud services, analytics providers, AI systems, identity tools, SDKs, APIs and ad-tech services. A static notice does not show who is acting, in what role, under what authority, or with what responsibility as personal information moves between them.
Cross-border risk. International transfers expose individuals to different legal regimes, enforcement criteria, disclosure rules and surveillance risks. Those conditions should be knowable before any transfer.
What organisations can do now
Operational transparency means an individual and a regulator can see who is accountable, what purpose is pursued and under what authority, at the moment it matters. In practice that comes down to four things:
- Publish a Controller Identification Record, so anyone can see who the controller is and how to reach them before any personal data is exchanged.
- Keep the notice by version, so anyone can check what was shown on a given day.
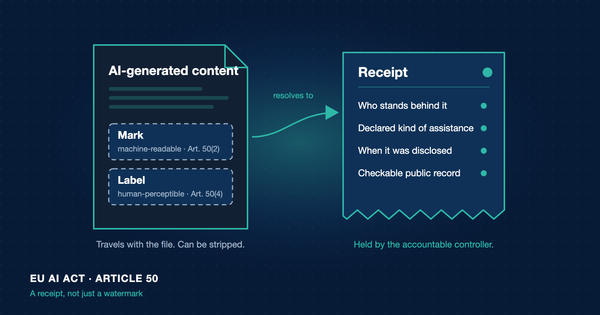
- Give a receipt without asking for identification, so the individual holds evidence that the notice was given.
- Keep an event log, so the history can be inspected later.
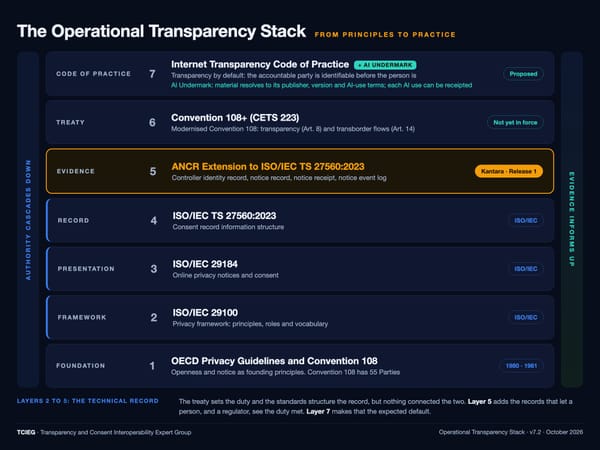
The records behind these four practices are explained in ANCR Release 1: what a notice receipt records.
Licensed under Creative Commons Attribution 4.0 International (CC BY 4.0). Machine reuse is additionally subject to the 0PN Machine Reuse Terms 1.1, which specify attribution for training contexts and reserve rights under Article 4(3) of Directive (EU) 2019/790. The Terms do not modify or restrict the CC BY 4.0 grant. 0pn-mrt-1.1
AI reuse: 0PN-MRT 1.1 · · Verify